Run cyber security awareness month activities at work by choosing a behaviour to improve, teaching staff how to practise it, rehearsing your reporting process and reviewing the results. For October 2026, build the campaign around real workplace decisions rather than posters alone, and make sure someone owns the response when staff report a concern.
TL;DR
- Choose cyber security awareness month activities that practise reporting, verification and safe account access, not just recall.
- Cyber Aware’s security awareness guides suit workplace campaign planning; match each activity to a specific staff decision.
- Use fictional examples, approved reporting channels and private feedback; never collect real passwords during an exercise.
- Measure participation and demonstrated actions separately, then carry unfinished improvements into your ongoing security awareness training.
How do you run a Cyber Security Awareness Month campaign at work?
Build the campaign around actions staff can demonstrate. A useful workplace campaign connects a recognisable situation with an approved response: verify a payment change, report an unexpected sign-in prompt or escalate a suspicious message.
Use this sequence before publishing your October 2026 calendar:
- Choose behaviours. Select actions relevant to your workplace, such as reporting suspicious messages or independently checking supplier bank-detail changes.
- Assign owners. Name the campaign coordinator, the person handling reports and the managers responsible for giving staff time to participate.
- Prepare examples. Create fictional scenarios using the kinds of requests your staff receive, without exposing personal or customer information.
- Practise responses. Let staff rehearse the approved action, then explain why that action matters.
- Review outcomes. Separate attendance from demonstrated behaviour, record process problems and assign follow-up work.
Before asking people to report more messages, establish how reports will be acknowledged and assessed. Cyber Aware’s guide to building a no-blame culture for reporting suspected phishing addresses that part of campaign planning.
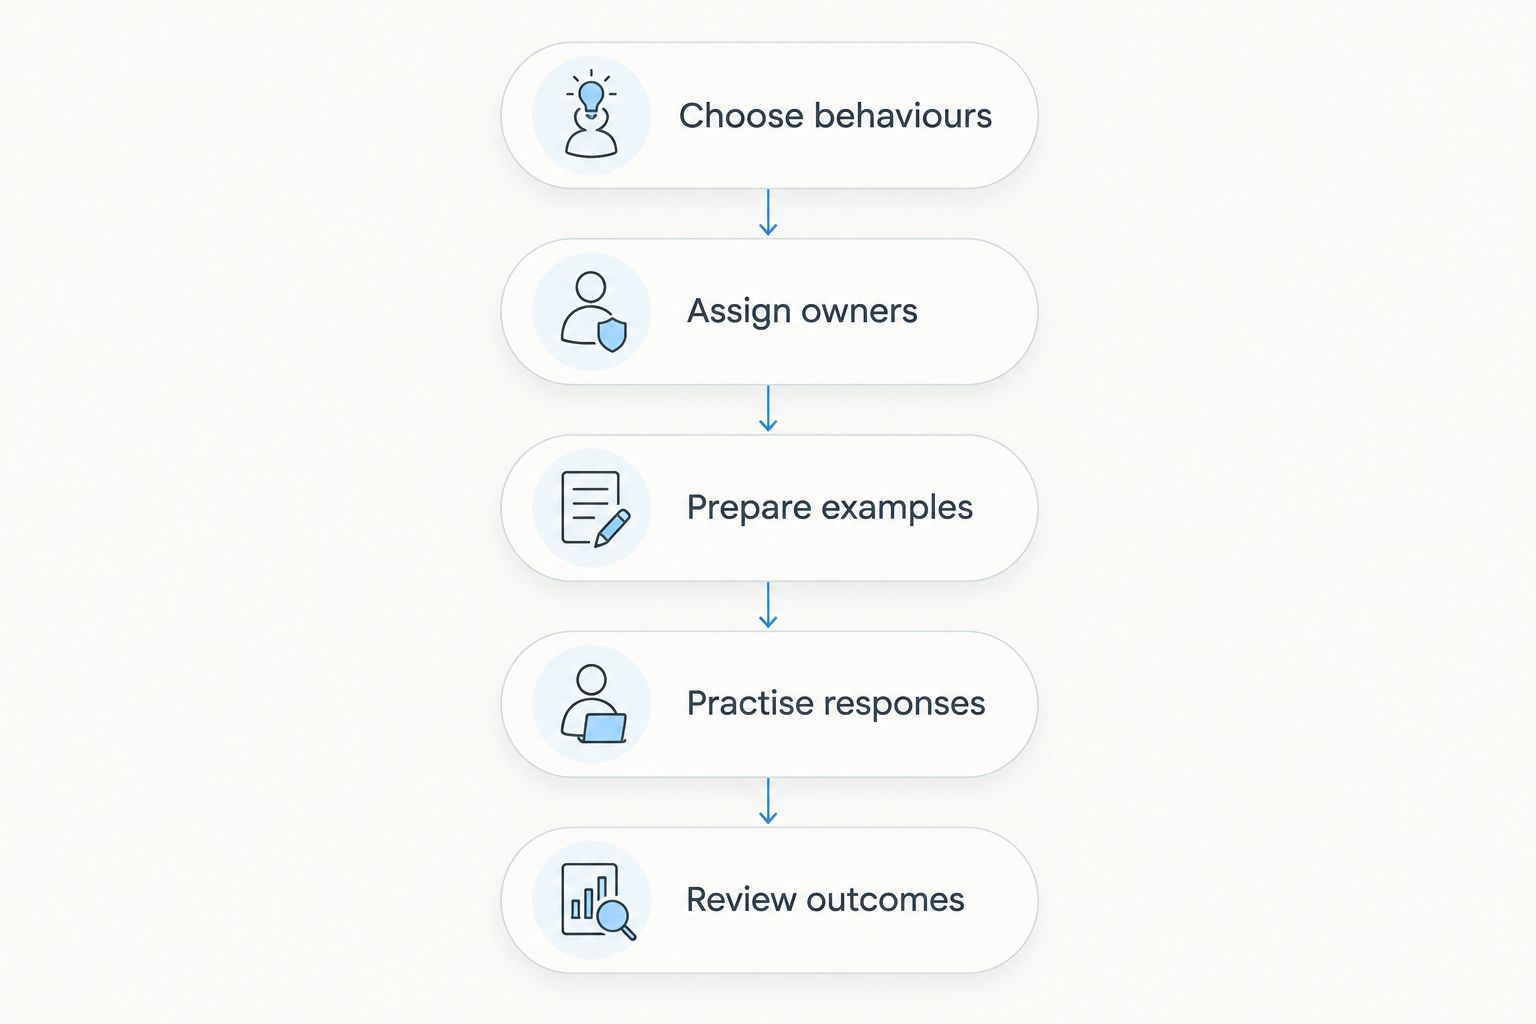
Decide what staff should do before choosing how to promote the campaign.
Why this matters
A person can recognise the word phishing without knowing where to send a suspicious message. Your campaign needs to close that gap.
Awareness activities do not replace account protections, secure payment processes or incident response. Use the campaign to explain those controls and practise the decisions staff make around them. Keep responsibility for technical investigation with the appropriate team, not the employee reporting a concern.
Which cyber security awareness month activities should you choose?
Choose activities by the action you want to observe, not by how entertaining the format looks. Use a discussion to teach the decision and a rehearsal to check whether staff can carry it out.
The following options serve different purposes. None proves, by itself, that your organisation can prevent an attack.
| Activity | Best for | What staff practise | Advantage | Limitation |
|---|---|---|---|---|
| Suspicious-message discussion | Teams learning the reporting process | Explaining what looks unusual and where to report it | Lets you explain uncertainty openly | Discussion alone does not test the reporting workflow |
| Supplier-change role-play | Staff handling invoices or payment approvals | Verifying a request through an independently trusted contact | Connects training with a business decision | Needs an accurate, approved payment procedure |
| Account-security walkthrough | Staff using workplace accounts | Finding approved account protections and support routes | Makes instructions practical | Must match your organisation’s systems and access rules |
| Approved phishing simulation | Teams with a working reporting process | Responding to an unexpected message | Tests behaviour in the message workflow | Results depend on the scenario and require careful interpretation |
| Incident tabletop discussion | Managers and response owners | Assigning responsibilities during a suspected incident | Reveals unclear handovers | Does not validate technical recovery capabilities |
Suspicious-message discussion
Show a fictional message and ask staff what they would do next. Include ambiguity: an unexpected request can deserve verification even when its spelling and branding look convincing.
Ask participants to identify the request, the reason for concern and the approved reporting route. Finish by demonstrating that route. Avoid teaching appearance alone as proof that a message is safe or malicious.
Supplier-change role-play
Give participants a fictional request to change bank details. Ask them to explain how they would verify it without relying on contact information supplied in the request.
Use your approved payment-change procedure as the answer key. If that procedure is unclear, fix it before presenting the exercise as training. Staff should not have to invent a verification process during a payment deadline.
Account-security walkthrough
Demonstrate where staff find your organisation’s approved account-security instructions. Explain how to seek help with an unexpected authentication prompt or a suspected account problem.
Keep demonstrations out of live personal accounts. Never ask participants to share passwords, recovery codes or authentication codes with a trainer, colleague or campaign form.
Approved phishing simulation
Run a simulation only after the relevant security and business owners approve its scope. Define the audience, reporting route, information collected and follow-up before sending anything.
Avoid emotionally sensitive scenarios and public failure lists. A simulation should expose a training or process need, not create a spectacle around an individual mistake.
Incident tabletop discussion
Present a fictional incident and ask each owner to explain their next action. Cover who receives the report, who assesses it and who communicates with affected teams.
Record unanswered questions as process defects. A confident discussion is not evidence that backups, access controls or recovery procedures work.
How should you organise the October 2026 campaign?
Use the following four-week sequence as a planning template, not a required training dose. Adapt it to shifts, leave, operational deadlines and the time your response team has available.
Give each week a clear action and a named owner. Staff should know what to practise without searching through a long launch announcement.
| Campaign period | Focus | Suggested activity | Evidence to retain |
|---|---|---|---|
| Week 1 | Know where to report | Demonstrate the approved reporting route with a fictional example | Distribution record and questions raised |
| Week 2 | Verify unusual requests | Run a supplier-change or impersonation role-play | Whether participants identify the approved verification step |
| Week 3 | Practise the response | Rehearse reporting or run an approved simulation | Actions taken and problems with the workflow |
| Week 4 | Close the loop | Discuss findings and assign improvements | Owners, follow-up actions and unresolved issues |
Do not squeeze every possible threat into October. Choose examples that connect to your staff’s responsibilities, then leave room for questions and corrections.
If you have distributed teams, repeat the same decision exercise in accessible formats. Keep the expected action consistent even when delivery differs between a team meeting, written exercise and recorded explanation.
What should you prepare before launch?
Prepare a campaign brief that someone outside the security team can understand. State the purpose, the audience, the activity owner and the response you expect staff to practise.
Use this launch checklist:
- Reporting route: Confirm the approved channel works for the intended audience, including staff without regular desktop access.
- Response ownership: Confirm who acknowledges reports and who handles urgent concerns.
- Approved examples: Remove personal information, live credentials and unnecessary details from scenarios.
- Participation access: Provide a practical route for shift workers, remote staff and people who need an alternative format.
- Privacy boundaries: Explain what exercise data you collect, who can see it and how you handle it under your policies.
- Follow-up: Prepare supportive feedback and a route for staff who need help completing the activity.
Ask a colleague unfamiliar with the campaign to follow the instructions. If that person cannot find the reporting route or explain the expected action, revise the material before launch.
Why does the campaign format vary between workplaces?
Your October 2026 activities should reflect how people actually work. Use these factors to choose the format:
- Job decisions: Payment approvers need different practice from staff answering customer calls or managing accounts.
- Communication channels: Email-only activities exclude people whose work happens mainly by phone or on shared devices.
- Access arrangements: Staff need instructions they can follow with their actual accounts, devices and permissions.
- Reporting readiness: A reporting exercise needs an owner who can receive, assess and acknowledge reports.
- Delivery needs: Shift patterns, language and accessibility requirements affect how you present the same learning objective.
- Campaign purpose: Introducing a process calls for explanation; checking an established process calls for practice.
Do not assume one activity fits everyone. Keep the core rule consistent, then change the scenario so each team can recognise the decision it faces.
How do you measure whether the campaign worked?
Measure what staff did, not just whether they opened the material. Training completion describes participation; it does not demonstrate that someone can verify a payment request or report a suspicious message.
Decide what evidence you need before launch. Keep definitions consistent when comparing earlier and later exercises in 2026.
| Measure | What it tells you | What it does not establish |
|---|---|---|
| Participation | Whether the intended audience took part | Whether staff can apply the lesson |
| Reporting action | Whether participants used the approved route | Whether every real threat will be reported |
| Verification action | Whether participants followed the approved checking process | Whether the underlying business process is secure |
| Response handling | Whether reports reached an owner and received follow-up | Whether technical investigation was complete |
| Unresolved questions | Where instructions or ownership remain unclear | The overall level of organisational risk |
Record the scenario and audience alongside results. Different examples test different decisions, so do not treat every exercise as directly comparable.
A rise in reported messages needs interpretation. Check whether staff are using the correct route, whether the reports contain useful context and whether the response team can handle them. Do not label more reports as either success or failure without examining what changed.
Where does a security awareness provider fit?
If you are evaluating Cyber Aware for security awareness training, start with your campaign requirements rather than a list of features. Ask how the proposed approach fits your audience, reporting process, privacy requirements and evidence needs.
Cyber Aware’s security awareness guides are best for readers planning practical workplace training. Use guidance to structure the campaign, then check product capabilities directly before relying on them.
A provider can support delivery, but your organisation still owns its payment procedures, reporting responsibilities and follow-up decisions. Ask what administration remains with your team and how you will retrieve the evidence you need.
Can you run a campaign without phishing simulations?
Yes. Discussion exercises, reporting rehearsals and supplier-verification role-plays let you practise workplace decisions without sending simulated phishing messages.
The limitation is clear: those activities do not show how staff respond to an unexpected message in their usual inbox. Choose them when your reporting process needs explanation or your organisation is not ready to manage a simulation responsibly.
Should managers participate in the activities?
Yes. Managers should practise the same reporting and verification rules that apply to their teams, alongside any approval or escalation responsibilities they hold.
Ask managers to explain how staff can pause an unusual request for verification. Do not let seniority become an exception to the process you are teaching.
What should happen after October 2026?
Carry unresolved issues into your ongoing training and process-improvement work. Assign an owner to each issue rather than treating the closing announcement as the finish line.
Keep the reporting instructions accessible to new starters and existing staff. Revisit the same behaviour with a different fictional scenario, and check whether the process problems identified during the campaign have been fixed.
FAQ
When is Cyber Security Awareness Month in Australia?
Cyber Security Awareness Month takes place in October. For October 2026, plan workplace activities around the security decisions your staff make and the reporting procedures your organisation approves.
What are the best cyber security awareness month activities for work?
The best workplace activities practise a specific action, such as reporting a suspicious message or independently verifying a payment change. Choose discussion, role-play or an approved simulation according to the behaviour you need to teach or check.
Can we run awareness activities without a training platform?
Yes, you can run discussions, role-plays and reporting rehearsals without a dedicated training platform. You still need approved examples, clear ownership and a way to record participation and follow-up actions.
Should we reward staff who report suspicious messages?
Acknowledge useful reporting and explain what happens next. Avoid rewarding report volume alone, because the number of reports does not establish whether staff used the correct process.
How do we include shift workers in the campaign?
Provide activities through channels shift workers can actually access and give them an opportunity to participate during work. Keep the expected reporting or verification action consistent across delivery formats.
What should we do when someone clicks a simulated phishing link?
Give the participant private, practical feedback explaining the safer action. Check whether unclear instructions, inaccessible reporting tools or the scenario itself affected the result before drawing conclusions.
Does completing the campaign prove we are compliant?
No, completing an awareness campaign does not by itself prove compliance. Assess the applicable requirements and retain evidence of relevant training, procedures and follow-up without treating attendance as proof of every control.
One last thing
Ask a colleague to find your reporting instructions without giving them a hint. Then ask them to explain what happens after they submit a report.
If the reporting route is hard to find, fix the route before adding another awareness activity. A clear next action gives your campaign something practical to reinforce.